

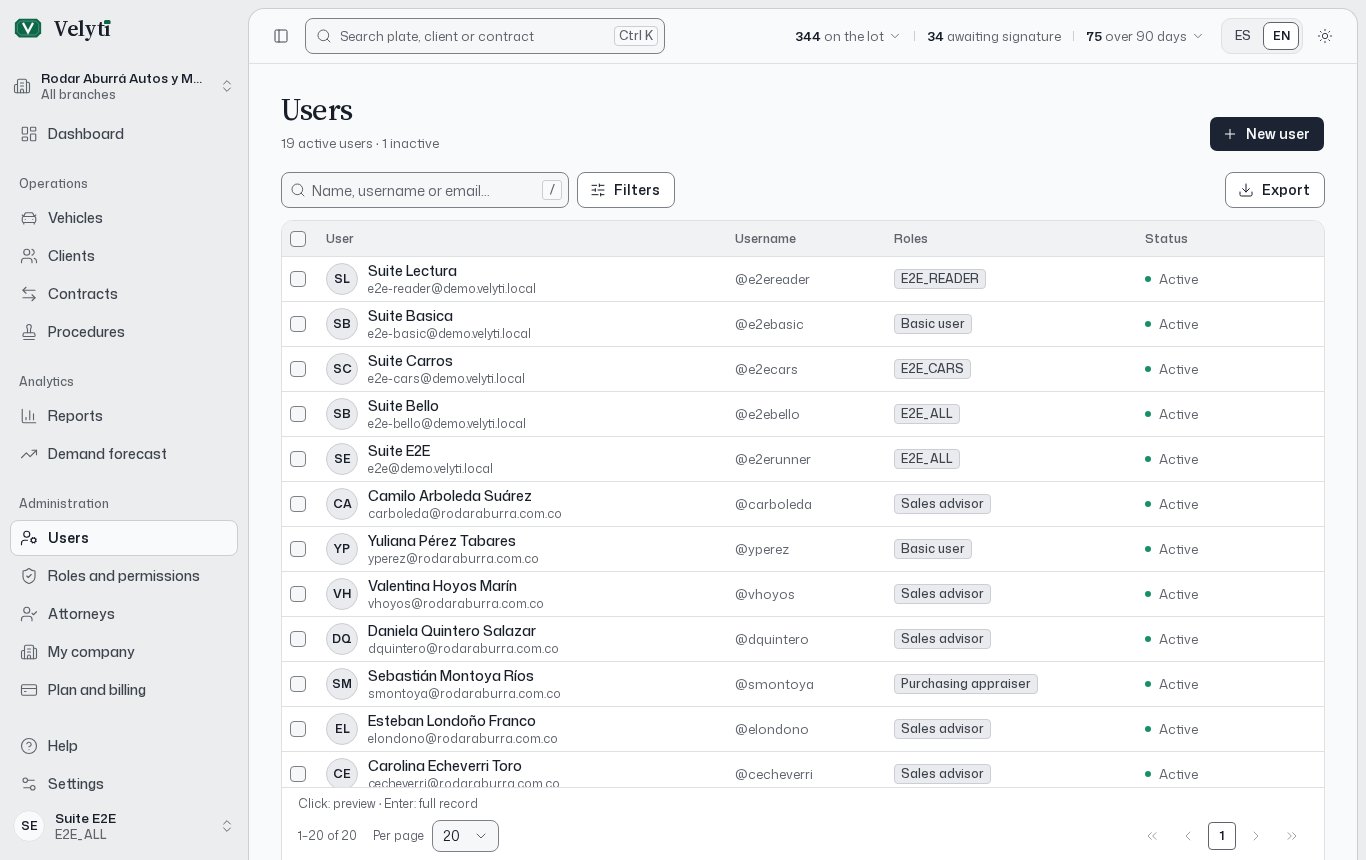
The Users list.
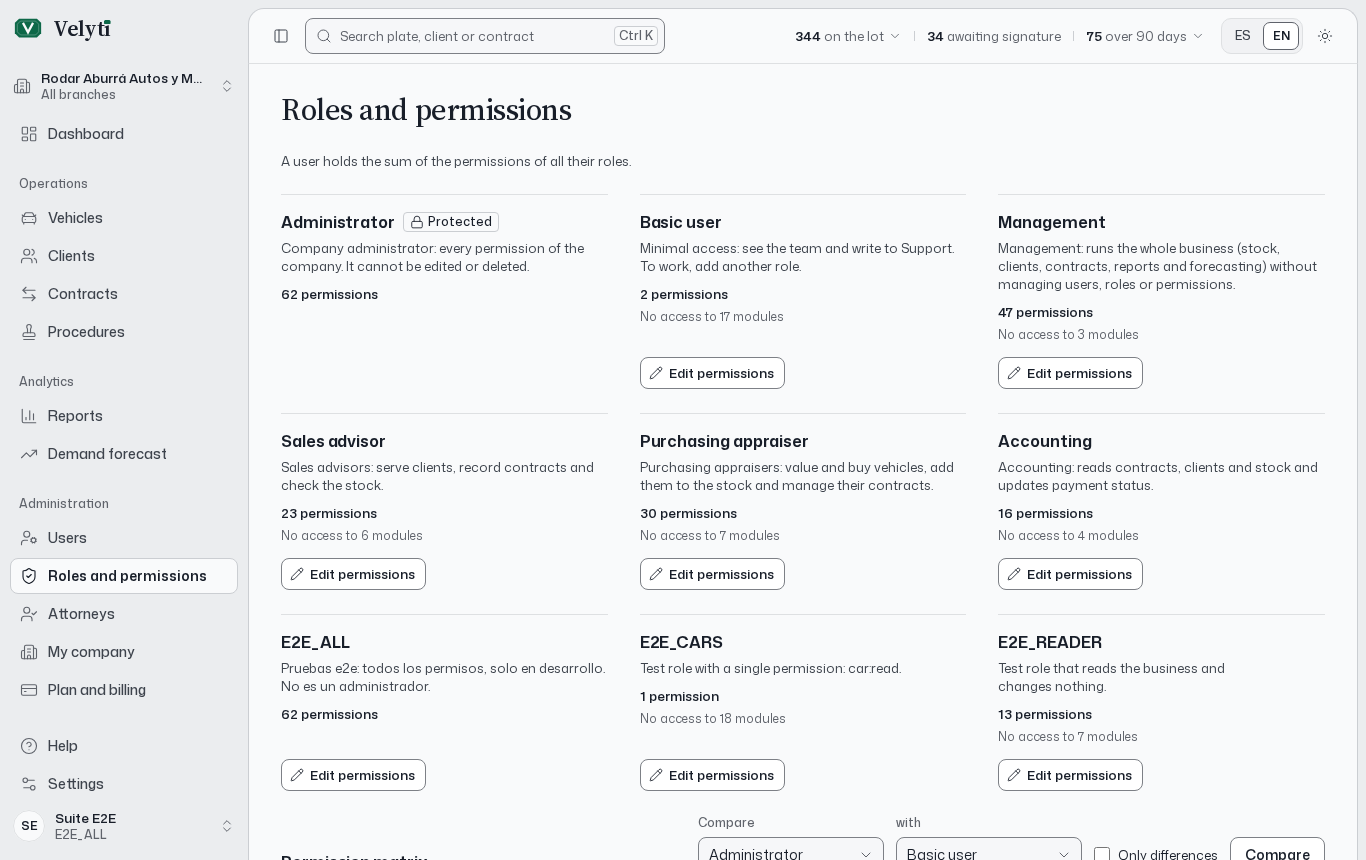
Roles and permissions.
Users
The Users page lists your team. Search by name, username or email, and filter by Any role or Any status. A summary shows how many users are active and how many inactive. Each user is Active or Inactive. An account that was invited and has not set its password yet shows Invitation pending, or Invitation expired if the link lapsed.Invite a user
1
Open the form
Choose New user.
2
Fill in the details
Enter the given names, last name, ID number, email and a Username. The username is unique across all of Velyti.
3
Choose the roles
Choose at least one role. A user may hold several roles, and their permissions add up.
4
Send the invitation
The app sends an email with a link to set a password. The link expires in 72 hours. Nobody types a colleague’s password: the person sets their own.
Branches
In a user’s record, Branches sets where they work: the branches whose vehicles, contracts and procedures they see and record. Choose Every branch (including those opened later) or Only these branches with at least one selected, then Save branches. You can only give branches you work in yourself, and only someone who works in every branch can give every branch. The change reaches their session within a few minutes.Deactivate, activate or delete
To stop someone signing in while keeping their name on the paperwork, deactivate them. Your plan may limit active users; see Plan and billing.
Roles and permissions
The Roles and permissions page lists the roles. A user holds the sum of the permissions of all their roles. The standard roles are Administrator, Basic user, Management, Sales advisor, Purchasing appraiser and Accounting.Read the permissions
Each role shows how many permissions it grants and how many modules it cannot access. Permissions are a resource and an action. The resources are Users, Roles, Permissions, People, Companies, Vehicles, Cars, Motorcycles, Contracts, Legal entities, Branches, Attorneys, Procedures, Documents, Forecast, Reports, Subscription, Support requests and Support access. The actions are Create, View, Edit, Delete, Manage, Predict, Retrain and Models, where each resource has the ones that apply. Some permissions are marked Sensitive because they give power over other people’s access. A role marked Protected holds every permission and cannot be edited or deleted.Compare roles
The Permission matrix lays the roles side by side. Use Compare to pick two roles and see only what differs, or Show all roles to go back.Edit a role
1
Open the role
Choose Edit permissions on the role.
2
Tick what the role can do
Click a resource name to grant or revoke the whole group.
3
Save
The change applies to everyone with that role within a few minutes.
Permissions you do not hold yourself appear locked: you cannot give them. Editing a role’s permissions also needs Permissions: View. If another administrator changes the role while you edit it, reload the page and apply your changes again.